

In recent months experts have seen many examples of sophisticated scam and phishing mailings, but that doesn’t mean that traditional, simple tactics have gone away. During the early weeks of the post-holiday season, Kaspersky’s team has uncovered an ongoing phishing campaign that impersonates Zoom and Docusign official emails.
This case demonstrates that sometimes spammers rely on tried and tested, basic phishing schemes, hoping that at least some of them will succeed.
In the first wave, attackers sent emails impersonating an official Docusign communication to corporate accounts across the Middle East, Latin America, Western Europe, Russia, Armenia and Azerbaijan, each containing phishing links designed to steal credentials.
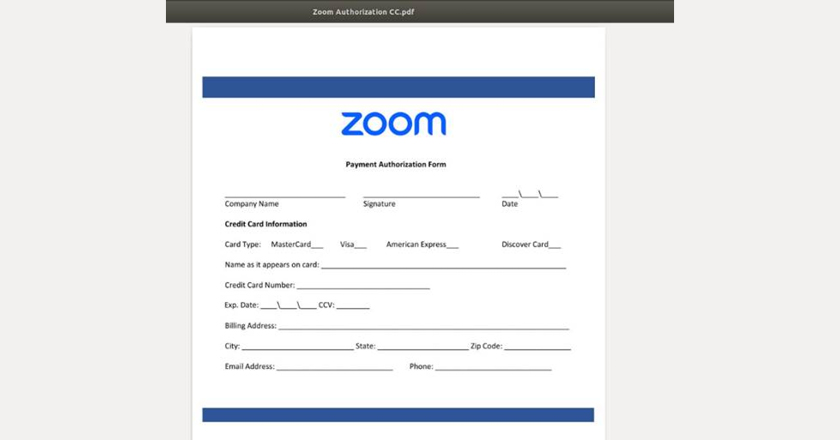
A second wave appeared a little more than a week later and continues to be active today. This time posing as official Zoom notifications, emails warn users that their accounts are about to be disabled. The campaign used two simple lures: phishing links that redirected recipients to credential‑stealing pages and embedded forms that solicited personal information and credit‑card details.
As of September 2026, more than a thousand phishing emails have been detected as a part of this campaign.
“In light of the pace of technological development and the widespread adoption of AI, we often tell people how to distinguish sophisticated fraudulent mailings and schemes. However old primitive methods are still being used and sometimes such simplicity can be effective as employees may overlook any phishing signs amid the massive flood of incoming mail, while fraudsters are choosing brands that are widespread in the corporate environment in order to successfully mimic real mailings. Even these low‑tech tactics should be caught by dedicated security solutions, so a company’s cyber safety doesn’t depend solely on the human factor”, notes Andrey Kovtun, Email Threats Protection Group Manager at Kaspersky.
To keep corporate environment secured Kaspersky experts recommend:
- Consider deploying a dedicated security solution that safeguards corporate emails from spam, email-borne infections, and all forms of phishing – such as Kaspersky Security for Mail Server. It addresses both traditional and modern phishing methods, using advanced heuristics that can identify AI-generated phishing attempts.
- Deliver security trainings for employees to raise their cyber awareness and reduce the risk of human-related incidents.
- Integrate an extended defense that combines endpoint threat protection with human-risk mitigation. Kaspersky Small Office Security Premium is specifically designed for smaller businesses: it prevents staff from being scammed by phishing, blocks malicious links, and includes a built‑in security awareness platform that educates employees.
- Regularly inform employees about potential cyber threats, highlight key features of a malicious message, and emphasize that phishing can disguise itself as the official emails.
- Conduct controlled phishing campaigns to test employee vigilance and identify high‑risk groups.
- Deploy multi‑factor authentication (MFA) for all email accounts, especially for privileged users and use password‑less options (e.g., tokens or mobile push) where possible.
Image Credit: Kaspersky
Source: Tahawul Tech